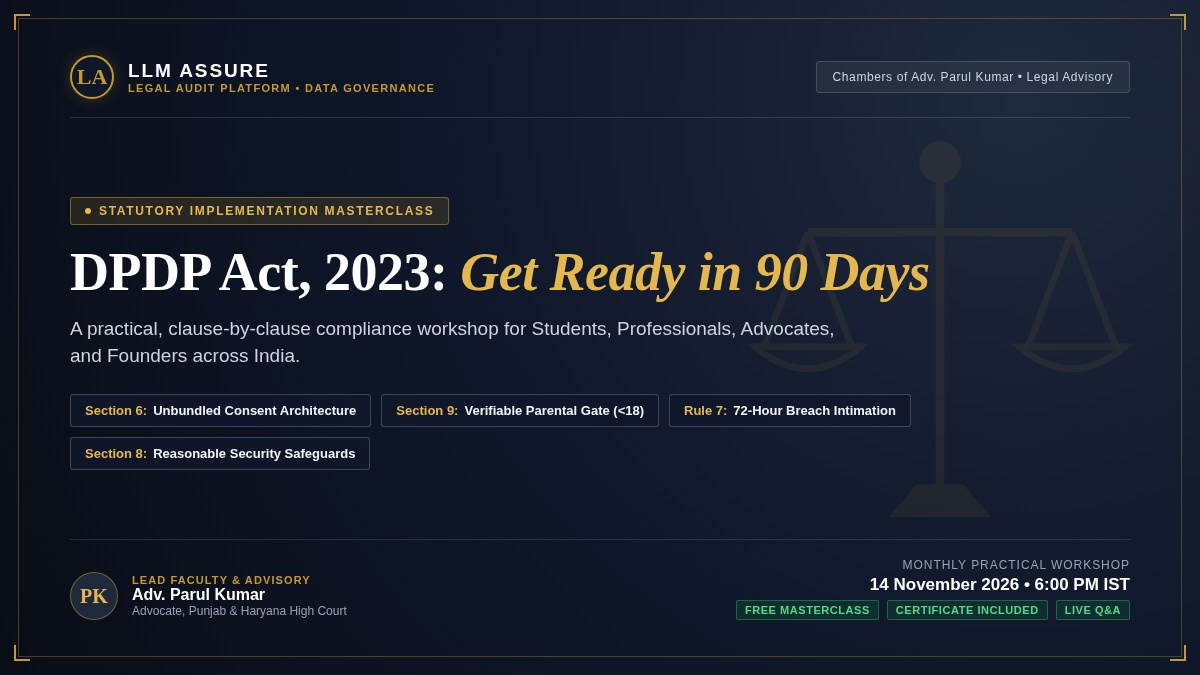
DPDP Act Webinar: A Practical Workshop for Students, Professionals and Founders
Understand India's Digital Personal Data Protection Act, 2023 and leave with working compliance documents. Whether you are a student, practicing advocate, software engineer, corporate executive, or startup founder — this hands-on workshop equips everyone with operational data privacy capabilities.
Why this matters
Enforcement Timeline
The DPDP Act, 2023, and the notified DPDP Rules, 2025, follow a phased commencement schedule. The principal operational provisions (Sections 3–17) take effect on 13 May 2027 (18 months from the 13 November 2025 notification), while certain institutional provisions commenced earlier. Starting preparation now gives technical and legal teams the runway to map data flows, draft notices, audit third-party processors, and operationalize rights mechanisms.
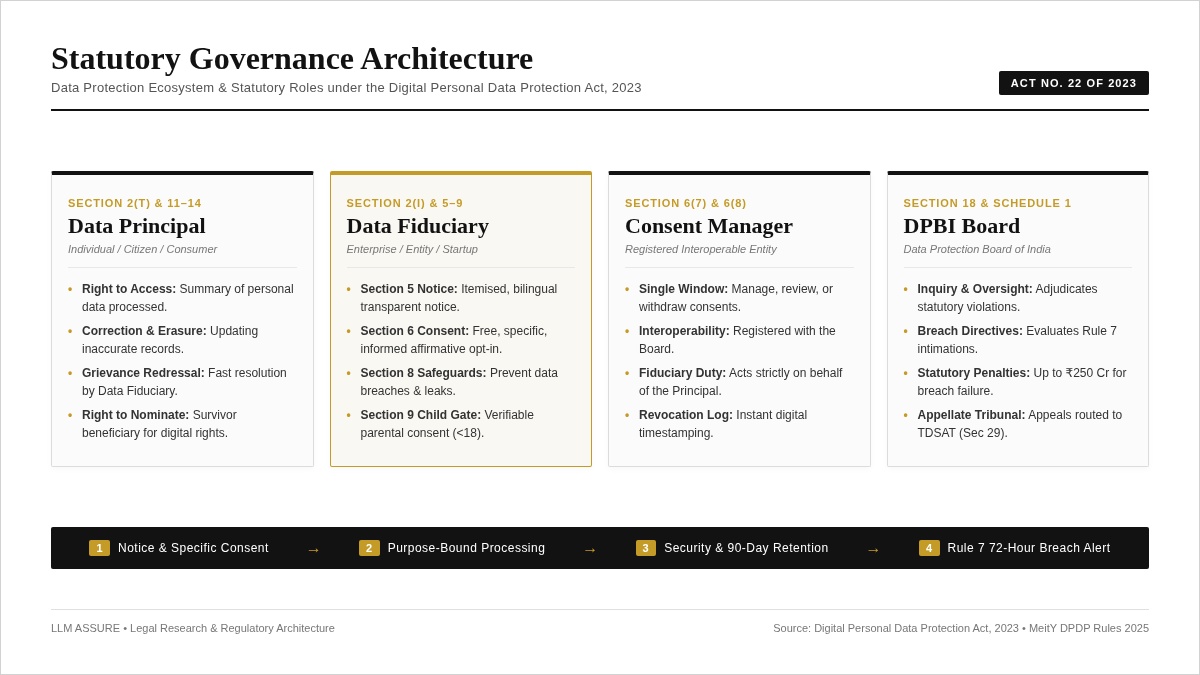
Statutory Penalties
Schedule 1 of the DPDP Act sets significant statutory maximum penalties: up to ₹250 crore for failure to take reasonable security safeguards to prevent a personal data breach, and up to ₹200 crore for failure to notify the Board or affected individuals. Penalties are determined based on statutory factors, proportionality, and mitigations rather than automatic flat fines.
Commercial Due Diligence
Enterprise customers, institutional partners, and investors increasingly evaluate privacy governance and security safeguards during vendor risk assessments and due diligence. Demonstrable compliance readiness helps organisations meet enterprise procurement expectations and avoid friction.
What you will do in the 45-minute workshop
Map key data flows in a live exercise
Begin building a structured data inventory across your product stack and vendors. Map personal data elements, identify collection purposes, and establish internal risk-based sensitivity classifications to guide security safeguards.
Review notice text and consent mechanisms
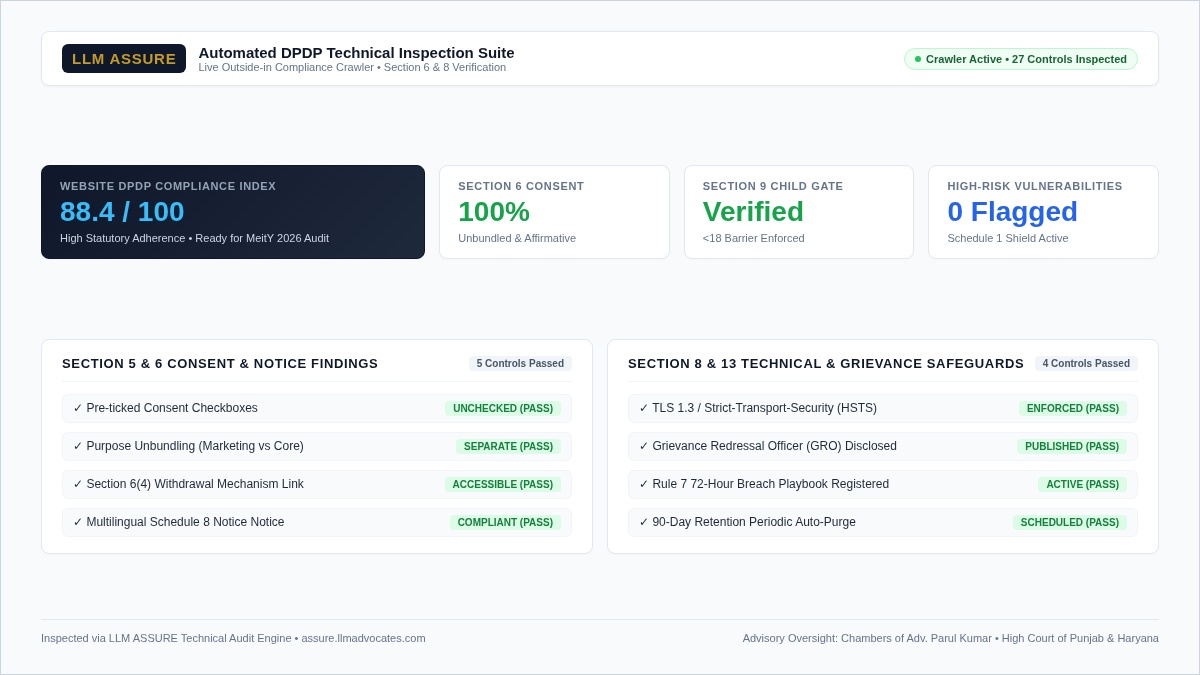
Learn statutory requirements of Section 5 (itemised notice) and Section 6 (free, specific, informed, unconditional, and unambiguous consent with affirmative action). Review onboarding consent text, unbundled marketing choices, and self-service withdrawal mechanisms.
Practise an incident-response drill
Practise the first six hours of an internal breach-response process: escalation, containment, evidence preservation, and impact logging. Distinguish internal response targets from statutory duties — including notification to affected individuals without delay, initial intimation to the Board without delay, and the 72-hour detailed report under DPDP Rules, 2025.
Evaluate real-world product workflows
Work through 5 practical scenarios (analytics cookies, marketing automation, third-party SDKs, AI/LLM integrations) against DPDP statutory benchmarks, backed by an annotated review key with statutory citations.
What you will take away
Subject to session completion, confirmed registrants receive a starter kit of working compliance drafts and operational checklists to assist internal implementation:
-
Data inventory sheet Structured spreadsheet template to catalog personal data flows, processing purposes, system owners, processors, and retention periods.
-
Consent and notice templates Purpose-specific notice drafts, affirmative consent-record structures, and withdrawal handling workflows.
-
Breach-response playbook Operational escalation guide covering internal containment, evidence preservation, impact logging, and statutory notification timelines under the DPDP Rules, 2025.
-
Vendor review checklist Contractual review checklist aligned with Section 8(2) processor obligations (processing instructions, security safeguards, incident notification, subcontracting, and data erasure).
-
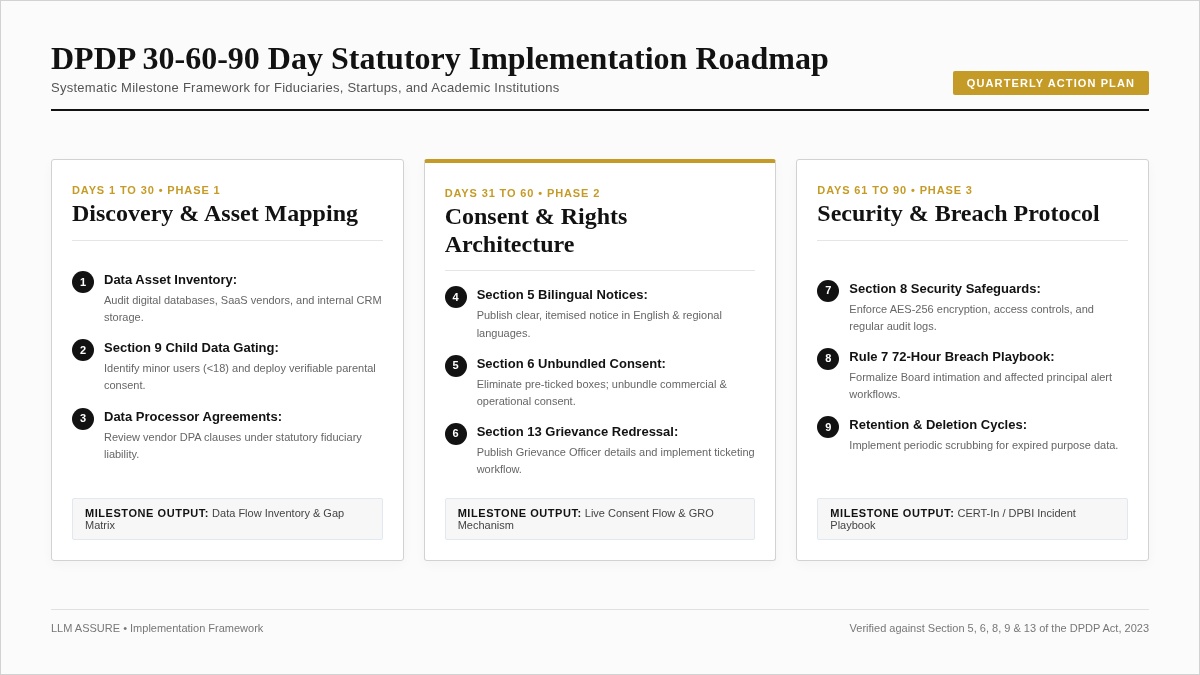
30-60-90 day roadmap Phased milestone framework mapped to the notified phased commencement schedule.
-
Readiness checklist Evidence-based assessment questionnaire to benchmark internal progress and identify gaps.
-
Session recording & deck Complete recorded video and slide deck available within 48 hours for confirmed registrants for internal team review.
Agenda
A structured 55-minute timetable: 45 minutes of intensive practical workshop followed by 10 minutes of live Q&A:
| Time (IST) | Topic & Activity | Focus Area |
|---|---|---|
| 6:00 – 6:05 PM |
Opening Poll & Benchmark
Quick pulse poll on attendee readiness, stack complexity, and current privacy postures.
|
Foundational check |
| 6:05 – 6:12 PM |
Framework & Statutory Penalties
Statutory duties of Data Fiduciaries, Section 5 itemised notices, Section 6 consent standards, and Schedule 1 penalty scope.
|
Statutory scope |
| 6:12 – 6:18 PM |
Security Safeguards Mandate
What constitutes "reasonable security safeguards" to prevent personal data breaches under Section 8(5).
|
Technical safeguard |
| 6:18 – 6:26 PM |
Data Inventory Workshop
Live mapping exercise: categorizing data fields across production databases and cloud tools.
|
Hands-on exercise |
| 6:26 – 6:33 PM |
Notice & Consent Workshop
Live text redrafting: auditing sample signup screens and composing compliant notice text.
|
Hands-on exercise |
| 6:33 – 6:39 PM |
Incident-Response Simulation
Internal escalation, containment, and statutory reporting under DPDP Rules (notification without delay & 72-hr detailed Board report).
|
Incident response |
| 6:39 – 6:43 PM |
Scenario Round
Interactive compliant-or-not evaluations of real startup growth tactics and analytics practices.
|
Applied scenarios |
| 6:43 – 6:45 PM |
90-Day Implementation Roadmap
Walkthrough of phased milestones for your engineering, product, and leadership teams.
|
Execution plan |
| 6:45 – 6:55 PM |
Q&A with Adv. Parul Kumar
Live questions answered directly by Adv. Parul Kumar on startup-specific DPDP ambiguities.
|
Open floor [10 mins] |
Before you attend
To maximize the practical outcome of this working session, please have these 3 items accessible:
Your signup screen
A screenshot or live web view of your current user onboarding, signup modal, or lead capture form.
Privacy policy link
The live URL to your current customer-facing privacy policy or terms of use agreement.
Customer data tools list
A simple list of external tools, CRMs, analytics trackers, and databases that currently hold customer data.
Who is this workshop for?
This practical workshop is designed for everyone seeking operational, technical, and statutory clarity on India's DPDP Act, 2023 — whether you are preparing for a career, advising clients, building software, or steering an enterprise:
About the speaker
Adv. Mr. Parul Kumar
Adv. Mr. Parul Kumar is a practising Advocate at the Punjab and Haryana High Court, advising enterprises, digital platforms, and startup leadership on regulatory jurisprudence, constitutional compliance, and institutional governance.
His practice encompasses statutory alignment under the Digital Personal Data Protection Act, 2023, data fiduciary obligations, cross-border data transfer regulations, and cybersecurity incident advisory.
Registration
Submit your details below to confirm attendance. Please review the itemised privacy notice beside the form.
Your Seat is Reserved
We look forward to welcoming you on 14 November, 2026 at 6:00 PM IST for "Get DPDP-Ready in 90 Days: A Practical Workshop for Everyone" with Adv. Mr. Parul Kumar.
DPDP Webinar Archive & Knowledge Network
LLM ASSURE conducts monthly DPDP compliance workshops for Indian startup founders, engineers, corporate counsel, and law students. Explore our past workshop archives, download presentation slide decks, and access statutory compliance resources:
DPDP Rules 2025: Enforcement Timelines & Fiduciary Governance
Comprehensive analysis of MeitY notified DPDP Rules 2025, the 18-month phased commencement leading up to 13 May 2027, and practical operational steps for data inventories.
Section 6 Consent Architecture & CMP Implementation
Deep dive into statutory valid consent under Section 6: free, specific, informed, unconditional, and unambiguous with clear affirmative action, plus unbundled marketing choices.
Personal Data Breach Response: Escalation & 72-Hour Reporting
Practical simulation of Rule 7 notification requirements: reporting to affected individuals without delay, intimation to the Board, and detailed 72-hour reporting protocol.
Supporting DPDP Statutory Guides & Research Articles
Deepen your compliance preparation with our free advocate-authored resources and statutory commentaries:
FAQ
The Digital Personal Data Protection Act, 2023 (Act No. 22 of 2023) is India's principal legislation for personal data privacy. It governs the processing of digital personal data within India, and data processed outside India if offering goods or services to Data Principals in India. It establishes statutory fiduciary obligations, valid consent standards under Section 6, mandatory security safeguards under Section 8, and enforceable individual rights under Sections 11–14.
The DPDP Act and the notified DPDP Rules, 2025 follow a phased commencement schedule published by MeitY on 13 November 2025. While certain institutional provisions commenced upon notification, the principal operational requirements (Sections 3 to 17) come into force on 13 May 2027 (18 months from notification). Preparing now gives technical, product, and legal teams the runway required to map data flows, draft notices, audit processors, and operationalize rights mechanisms.
Schedule 1 of the Act establishes significant statutory maximum penalties: up to ₹250 crore for failure to take reasonable security safeguards to prevent a personal data breach, and up to ₹200 crore for failure to notify the Data Protection Board or affected individuals. Penalties are adjudicated by the Board based on statutory criteria, proportionality, and mitigations rather than automatic flat fines.
Under Section 5, every Data Fiduciary must give Data Principals an itemised notice before or at the time of requesting consent. The notice must clearly describe the categories of personal data to be processed, the specific purposes of processing, the manner in which the Data Principal may exercise their rights under Sections 11–14, and the contact details of the Grievance Redressal Officer.
Under Rule 7 of the notified DPDP Rules 2025, in the event of a personal data breach, the Data Fiduciary must notify affected Data Principals without delay, provide an initial intimation to the Data Protection Board of India without delay, and submit a detailed report to the Board within 72 hours of becoming aware of the breach.
Yes. Students and individuals are recognized as Data Principals entitled to statutory rights of access, correction, erasure, and grievance redressal. Educational institutions, ed-tech platforms, and universities processing digital student data are Data Fiduciaries subject to Section 9 verifiable parental consent requirements for minors under 18 and Section 8 security safeguards.
Yes. A recording of the complete session will be made available to confirmed registrants within 48 hours following the live broadcast, accompanied by the workshop slide deck, downloadable compliance templates, and a verifiable participation certificate.
No. This webinar provides general regulatory information, compliance frameworks, and operational templates for educational purposes. It does not constitute formal legal counsel or create an advocate-client relationship. Organisations should obtain tailored legal counsel for specific corporate circumstances.